Ownership change
The listed author or contributor list no longer matches the stored snapshot. A dropped original author means the handover is already complete.
Touchstone reads the public WordPress.org directory and the public plugin SVN repository, and tells you when a plugin on your site changes hands.
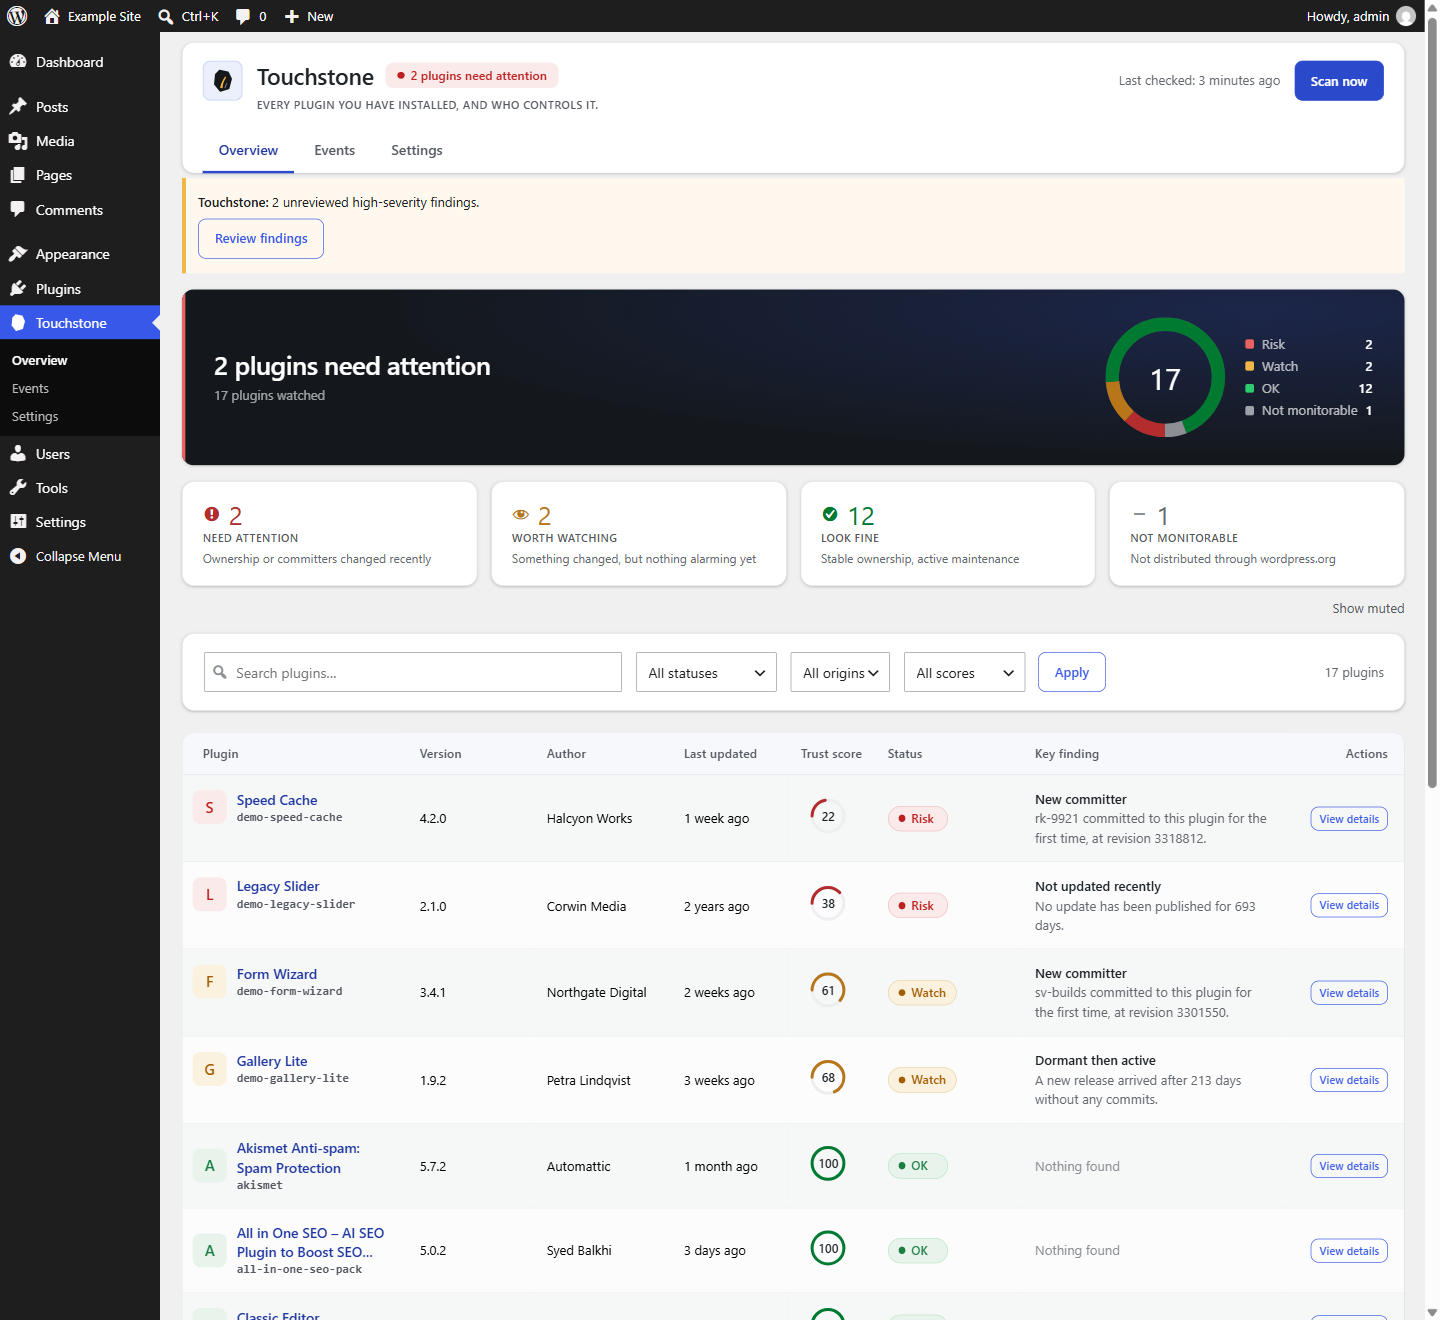
When a plugin is sold, WordPress.org performs no audit and sends no notification. The new owner inherits commit access, and their first release reaches every site running it through the ordinary update channel.
In April 2026 the WordPress Plugins Team closed 31 plugins at once. A single buyer had acquired the portfolio through Flippa, planted a backdoor across all of them, and waited. Most of those sites were running a vulnerability scanner the entire time, and a scanner has nothing useful to say about a plugin whose code has not turned malicious yet.
A transfer is not an attack. It is the window in which one becomes possible — and the only moment at which you still get to choose.
Three steps, once a day, entirely from public sources.
On the first scan it inventories every installed plugin and reads back up to 200 commits of SVN history, recording each committer with their first and last revision.
Recorded plugin-slug · committer-a r1–r2981 · committer-b r302–r2104
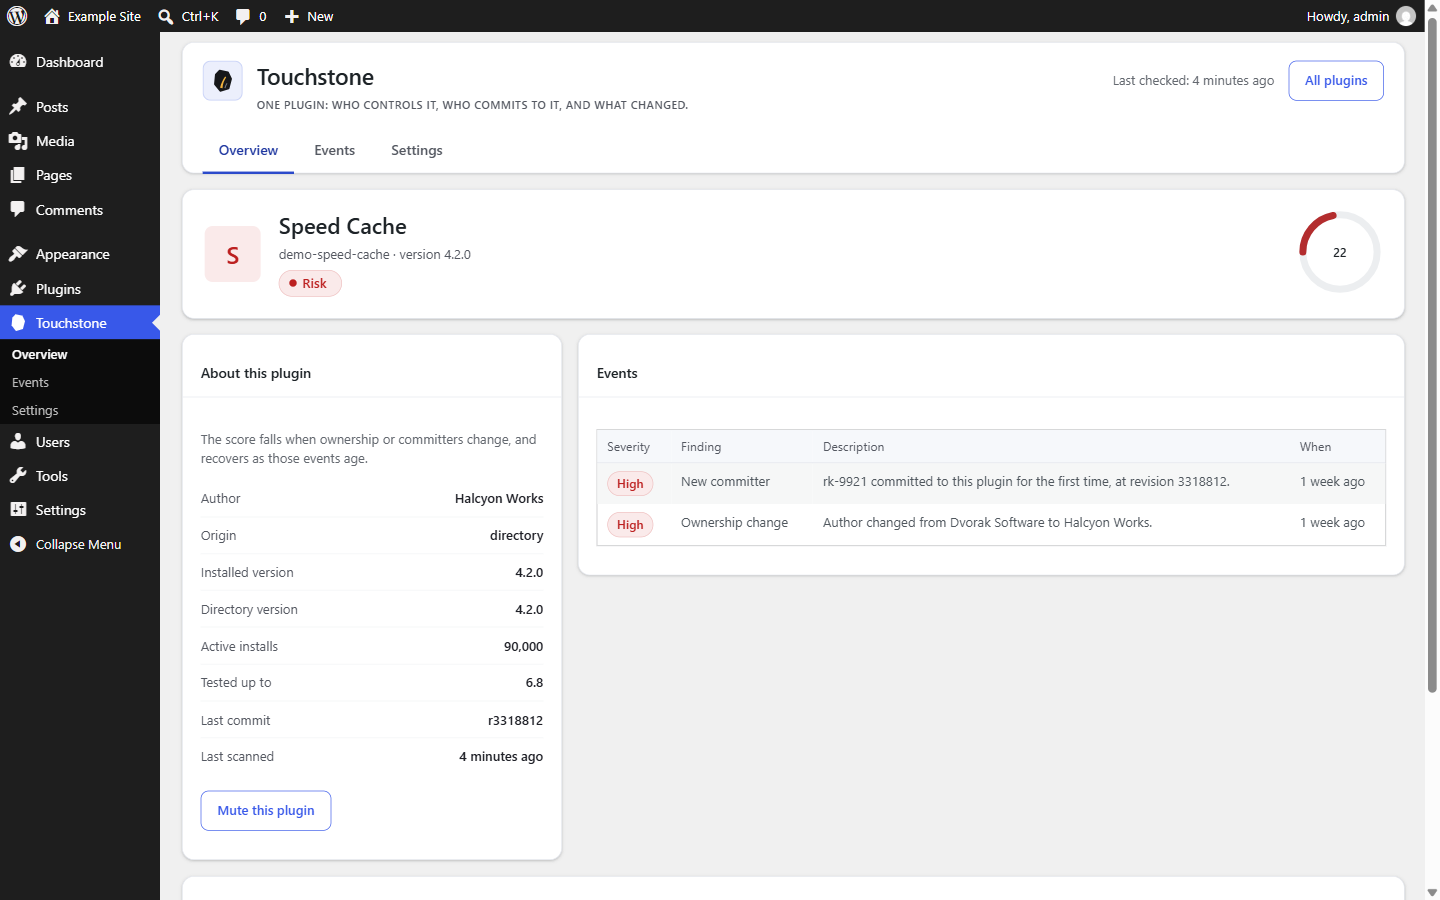
Every day it re-reads both public sources and diffs them against the stored record. A name that was not there before is the signal; five rules decide what kind of signal it is.
Changed author replaced · +1 unseen committer at r2982
The trust score moves, the plugin rises to the top of the list, and an admin notice appears for a high-severity finding. You acknowledge it, mute the plugin, or go and look.
Scored trust 94 → 61 · band ok → watch
Scans run on WP-Cron, ten plugins at a time, never during a front-end request. Your visitors never touch this code.
Each one watches a trust boundary, and fires before any payload can ship.
The listed author or contributor list no longer matches the stored snapshot. A dropped original author means the handover is already complete.
A previously unseen SVN username has committed for the first time. This is the event that precedes a payload, usually by weeks or months.
180 days of silence followed by a commit. Escalates when it lands alongside an ownership change or a new committer.
No update in 365 days, escalating past 730 — and fires again if the plugin is removed from the directory entirely.
The plugin is not in the directory, so it has no public history and cannot be monitored. It is listed as a blind spot rather than given a grade it has not earned.
Every plugin carries a deterministic score from 0 to 100. Same inputs, same score, with nothing you cannot explain to the person paying the invoice.
0/100
Band boundaries are fixed and published.
No new dashboard to log into, and nothing for your client to learn.
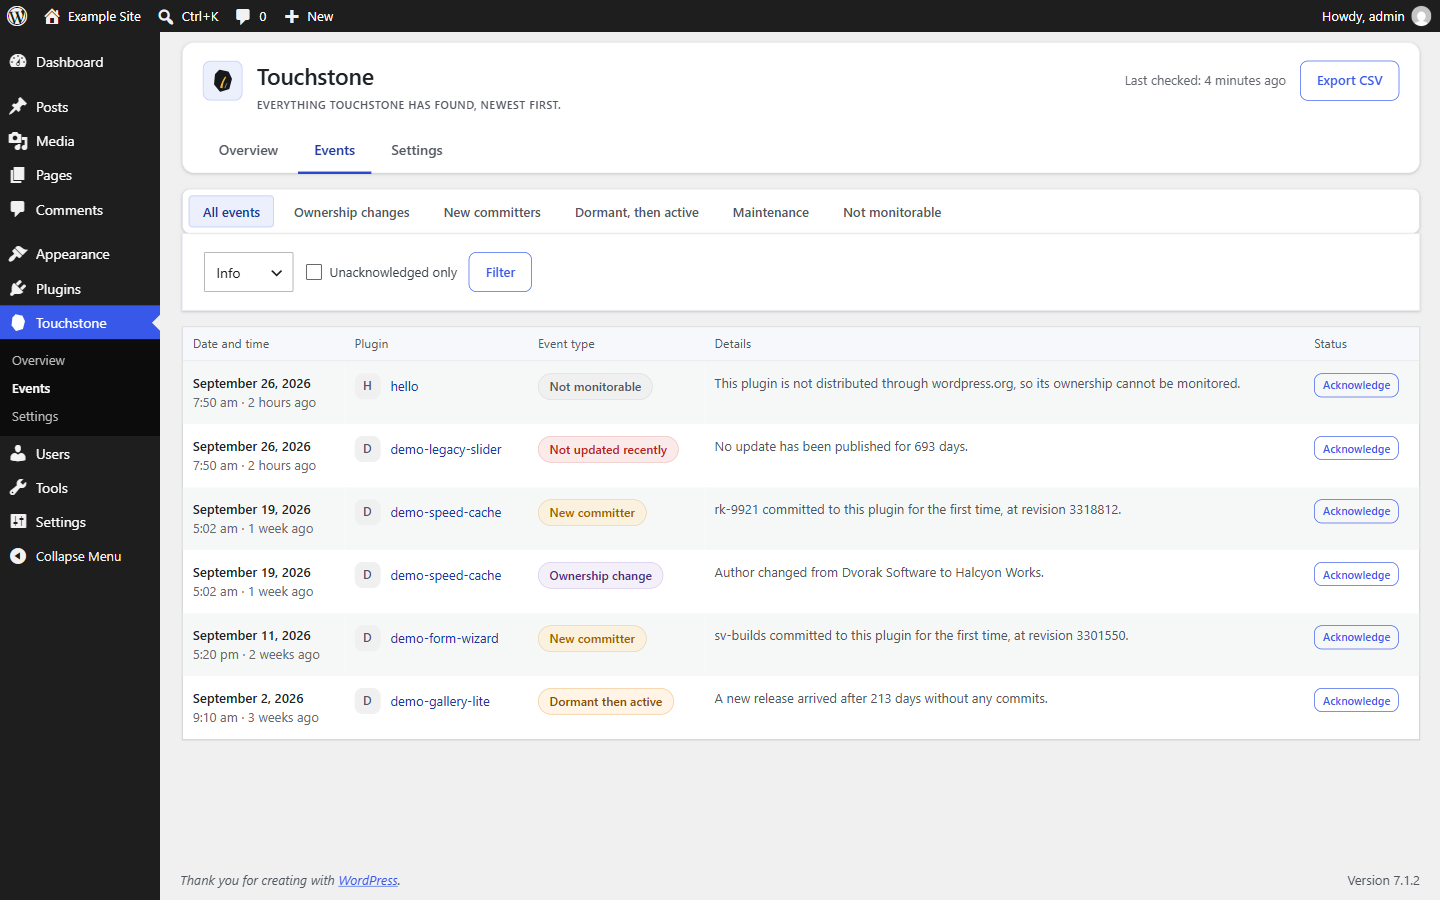
There are no certifications on this page because there are none to show. Here is the whole mechanism instead.
A plugin slug is the only thing sent to either. Open them in a browser and you will see exactly what the plugin sees.
GPLv2, so the source is in front of you. The free build contains no licensing code at all.
Every rule, every score, every screen, on every site, with nothing held back to sell you later.
Available now
$0forever
In development
$59/yr, 5 sites
In development
$179/yr, 25 sites
Pro and Agency are planned, not purchasable. Neither has shipped, and neither will ever live inside the free plugin — WordPress.org forbids paywalls in a hosted plugin, which is why the free build carries no licence code at all.
They detect known vulnerabilities and malware signatures, which means something bad has already been written. Touchstone detects the trust-boundary event — an ownership transfer, a new committer — that precedes it. They work a different layer of the same problem, so run them alongside this rather than instead of it.
Manually: open the plugin’s WordPress.org page, read the listed author and contributors, then open its SVN development log and compare the committer usernames against what you saw last time. That works for one plugin, once. Touchstone does it for every plugin on your site, every day, and tells you only when something changed.
No. Scans run on WP-Cron in small batches, ten plugins per tick by default, with API responses cached for twelve hours, so nothing is ever fetched during a front-end page load and the plugin produces no public-facing output at all.
Plugin slugs, to api.wordpress.org and plugins.svn.wordpress.org. That is the complete list. No telemetry, no analytics, no phone-home, no licence check. It is disclosed in the readme under External Services, and you can verify it in the source.
Not in the free plugin, and that is deliberate — it observes, it does not intervene. Update quarantine is the anchor feature of the planned Pro add-on, which would hold an update for review after a trust event fires. It has not shipped.
Most are, yes. So you acknowledge it once and it deducts nothing from the score ever again, or you mute the plugin entirely. Staying quiet until something genuinely changes is the whole design — an alert you learn to ignore is worse than no alert.
They have no public commit history, so they cannot be monitored. They are listed as unknown origin and counted as a blind spot rather than given a grade they have not earned.
Touchstone is finished and in review at WordPress.org. When it lists, it will find yours within a day.
Coming soon to WordPress.orgFree and GPLv2. Requires WordPress 6.2 and PHP 7.4 or newer.